PMA Lab 6-2: C Code Constructs in Assembly
Analyze the Malware found in the file Lab06-02.exe.
Lab 6-2
Analyze the Malware found in the file Lab06-02.exe.
1) What operation does the first subroutine called by main perform?
The first subroutine called by main (sub_401000) is the same we observed before in Lab06-01.exe. It checks the connected state of the system.
2) What is the subroutine located at 0x40117F?
Once again, at 0x40117F we have the “printf” function just like in Lab06-01.exe.
3) What does the second subroutine called by main do?
The second subroutine called by main is sub_401040:
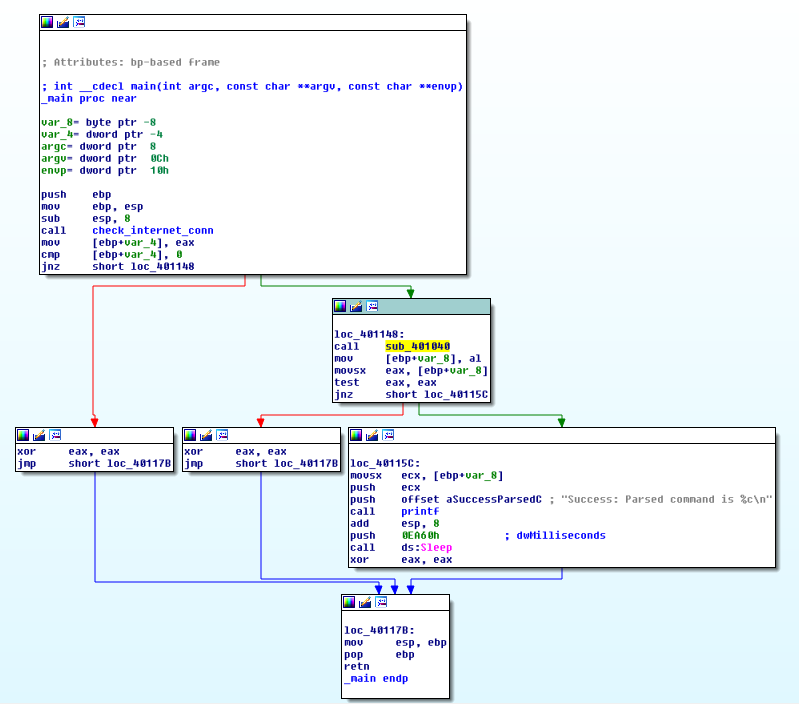
Let’s jump inside this function and take a look:
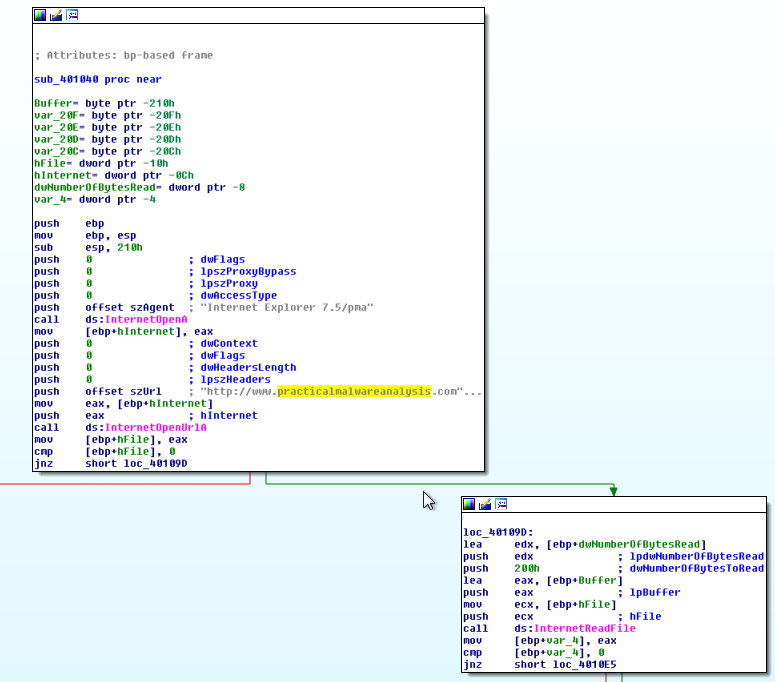
This subroutine starts by trying to connect to the Internet. In this case to the URL:
This request is made with a custom User-Agent:
- Internet Explorer 7.5/pma
These can be used as Network-based Indicators.
If InternetOpenURLA is successful, InternetReadFile is called:
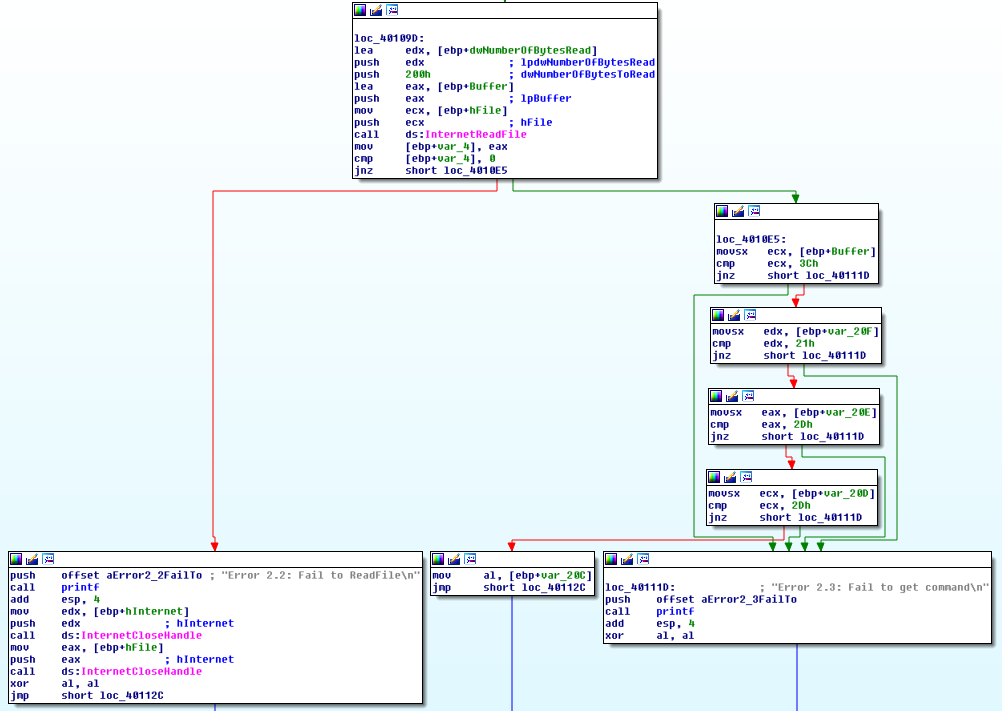
If InternetReadFile is successful we can see several comparisons taking place. If we take a close look at the offsets of the variables that are being compared and the bytes being compared we can see that the Code is attempting to check if whether it’s reading an HTML commentary or not:
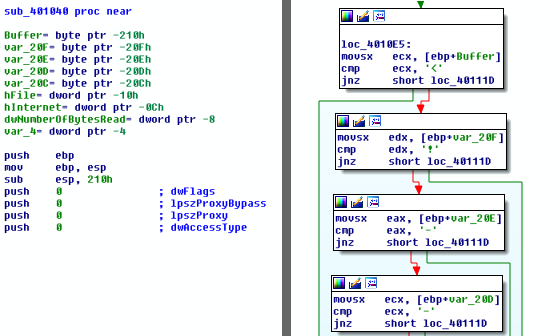
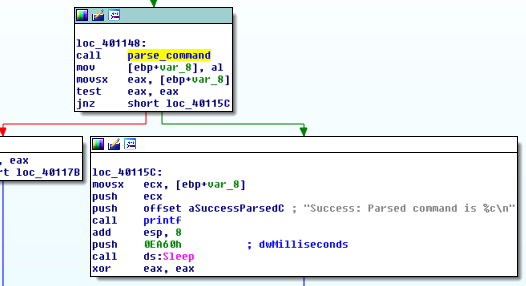
If every comparison is successful, var_20C (the address immediately after the HTML commentary) is returned by this subroutine. Because of this and the string that is printed in case this function doesn’t return NULL we can rename it to parse_command:
4) What type of code construct is used in this subroutine?
This subroutine contains an Array that will be populated with the content retrieved from the Web Page.
5) Are there any network-based indicators for this program?
This Malware tries to connect to the Internet:
The requests made by the Malware use a custom User-Agent:
- Internet Explorer 7.5/pma
These can be used as Network-based indicators.
6) What is the purpose of this Malware?
The purpose of this Malware is to retrieve commands from a Web page. The command is hidden in a commentary.